Cybersecurity experts say incidents had minimal effect but may represent the ‘foothills’ of a wider threat
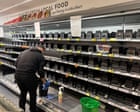
Meat suppliers in the UK have been hit by cyber-attacks after hackers raised the temperatures of supermarket freezers across Europe.
The UK’s National Cyber Security Centre said it was working with the affected companies but the national impact was minimal.
Speaking at the launch of the NCSC’s annual review on Tuesday, its director of operations, Paul Chichester, said: “We’re aware of those incidents in the UK, and obviously we’re working with the affected organisations. We’ll keep monitoring that. At the moment, the impact is minimal.”
Cybersecurity experts meanwhile reported that attacks on “dummy” fridge controls – deliberately placed online to lure would-be hackers – displayed characteristics similar to malicious operations linked to Russia.
Retailers in Belgium, Estonia, Ireland, Finland, Luxembourg, the Netherlands and Sweden reported problems with their refrigeration systems on Monday – with some rising to as high as 50C (122F) – and several companies confirming they had been hacked. Similar incidents were reported in France last month. It has emerged that the cyber-attack on French supermarket fridges involved legacy technology connected to internet with default passwords.
No UK grocery chain has been directly affected so far.
Chichester said the NCSC, part of the GCHQ spy agency, was working with organisations to identify loopholes in their technology and close them before hackers exploited them.
He said the NCSC was not able to comment on who might have carried out the attacks, but that they were not AI-enabled and had used vulnerabilities that had been “out there for a long period of time”.
The NCSC’s chief executive, Richard Horne, said the fridge attacks represented the “foothills” of an enlarged cyberthreat that companies and the public faced as AI systems highlighted flaws in IT networks that owners were not aware of or had neglected to patch.
“There are so many vulnerabilities out there that … you could say are waiting to be exploited,” he added.
The agency’s chief technology officer, Ollie Whitehouse, said everyday domestic devices connected to the internet would be susceptible to hackers in certain situations. He said manufacturers needed to be encouraged to make their technology safer, and consumers needed to accept paying more for safer equipment.
The British Association of Independent Meat Suppliers said some of its more than 300 members had been affected after becoming “collateral” in the hack.
The industry body said no meat had been lost in the refrigeration hacks but the incidents were a “reminder to all in the food industry at whatever point in the supply chain they are that their businesses may be seen by some as targets”.
One supply company saw its cold units rise to up to 100C (212F) while another two reported their units had started to defrost. The association said the affected units were empty at the time. The Grocer, a trade publication, also reported that a fruit and vegetable wholesaler in London had been affected but did not lose any stock.
Cybersecurity researchers said attacks on dummy Danfoss fridge controls – which were targeted by the hackers in mainland Europe – were similar to recent operations linked to Russia. Xavier Bellekens, the chief executive of the cyberdefence firm Lupovis, said it had recorded 256 attempted attacks from 91 different sources between 20 October and 30 October after setting up online “honeypot” traps that are indistinguishable to attackers from real Danfoss fridge controllers. The attackers attempting to gain control of the dummy controls remained anonymous, but most of the authentication attempts used the manufacturer’s publicly documented factory-default username and password credentials.
They also used what Bellekens called “bulletproof” hosting, which means using internet service providers that are particularly tolerant of malicious activity, often ignore abuse complaints or make it difficult for authorities to disrupt their customers’ operations. “What caught our attention was the overlap between infrastructure involved in the recent probing activity and infrastructure we have previously associated with Russian-linked malicious operations,” he said.
“While we are not able to pinpoint a group yet, the number of actors that fit this bill is relatively small and the bulletproof hosting we have seen being used by these actors for probing was also being used by Russian groups some time ago.”